Information security and firewalls
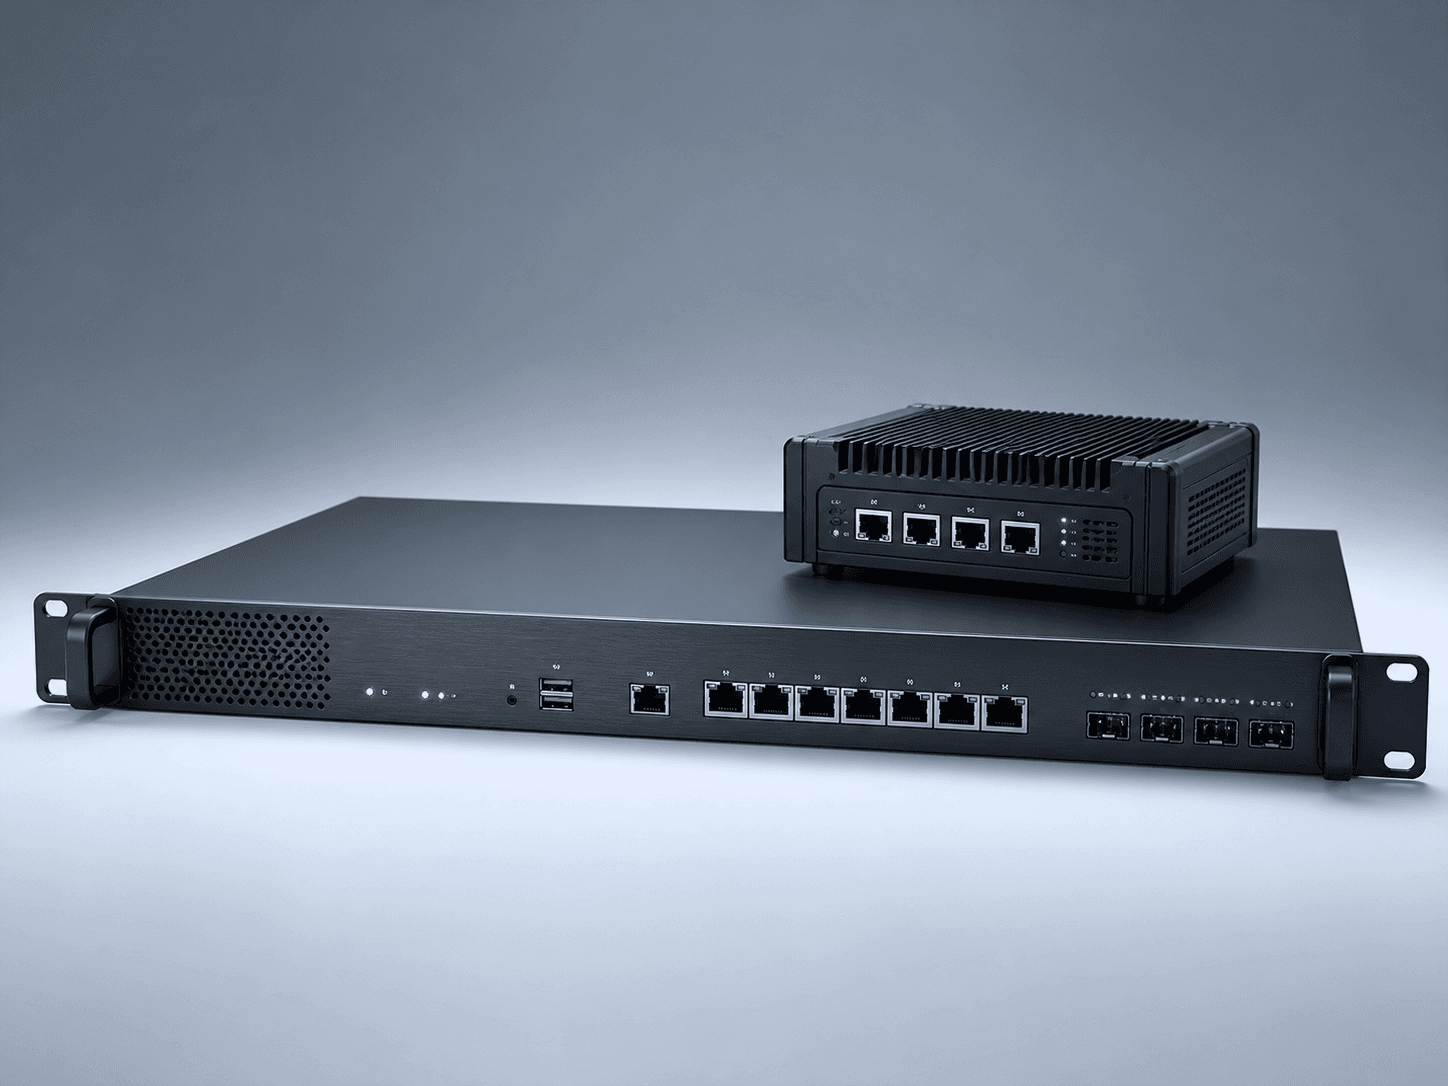
We select firewalls, security gateways, and protected-access equipment against network architecture, workload, and segmentation requirements. Licensing, interfaces, resilience, and integration with the existing environment are reviewed together.
Main subcategories
Firewalls
Security gateways
VPN and protected access
Policy management
High availability
Customer tasks
- 1Segment network zones
- 2Control external access
- 3Protect branch connectivity
- 4Keep policies manageable
Typical usage scenarios
- Organization perimeter
- Protected branch sites
- Remote access
- Service segmentation
Non-standard security perimeters
We can consider high-availability clusters, specific cryptographic requirements, remote sites, and platform migration. Applicability and licensing scope are confirmed after review.
Security equipment from a specification
We capture throughput, connection counts, interfaces, VPN scenarios, segmentation rules, redundancy, logging, and license terms.
- 1Receive requirements
- 2Check mandatory characteristics
- 3Clarify ambiguous requirements
- 4Select suitable options
- 5Check compatibility
- 6Agree scope and conditions
Discuss the security perimeter
Send the network diagram and requirements for throughput, segmentation, and current access policies.
Related services
- Network diagram review
- Licensing review
- Segmentation planning
- Configuration and validation